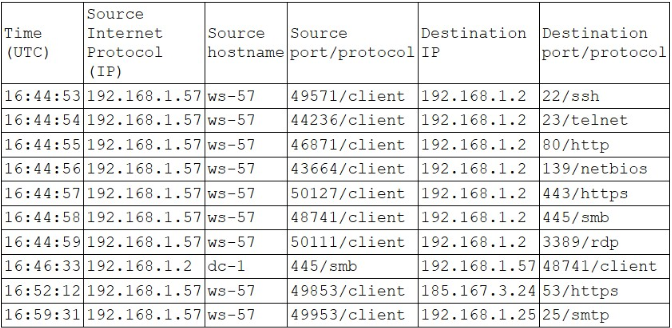
The log entries show ws-57 rapidly connecting to dc-1 across a wide range of well-known service ports (SSH, Telnet, HTTP, NetBIOS, HTTPS, SMB, RDP) within seconds of each other — this pattern of touching many ports in quick succession is characteristic of a network/port scan being run by ws-57 against dc-1. Separately, one log entry shows ws-57 communicating with an external host on destination port 53, but the protocol is identified as HTTPS rather than DNS, which normally uses port 53 — this indicates HTTPS traffic being tunneled or run over a non-standard port to potentially evade detection or firewall rules based on typical DNS traffic assumptions.
Community Discussion