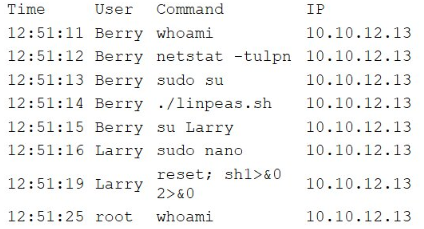
The log entries show a classic Linux privilege escalation chain: initial reconnaissance commands (whoami, netstat -tulpn), an attempt to elevate via 'sudo su', execution of linpeas.sh (a widely used privilege escalation enumeration tool that identifies exploitable misconfigurations and SUID/sudo binaries), lateral movement to another account ('su Larry'), and abuse of 'sudo nano' — a binary listed in GTFOBins that can be leveraged to break out into a root shell when sudo permissions are misconfigured. The final log line showing 'root whoami' confirms the attacker successfully escalated from a standard user to root. This progression of enumeration and exploitation of sudo/SUID misconfigurations to gain higher-level access is the defining characteristic of privilege escalation, as opposed to exfiltration (data theft), remote code execution (running arbitrary code via a vulnerability), or spoofing (impersonating a trusted entity).
Community Discussion