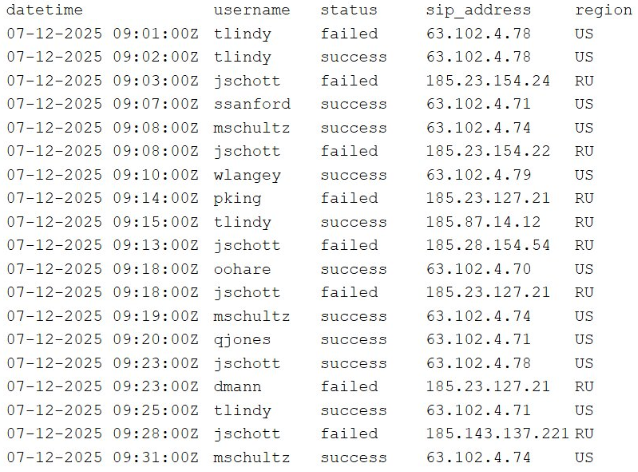
tlindy's log entries show a successful authentication from an IP address geolocated to Russia (185.87.14.12) sandwiched between successful logins from a legitimate US-based IP address. Because the organization is based in the United States, a successful login from an unexpected foreign region strongly suggests the account credentials were compromised and used by an unauthorized actor — this is a confirmed anomalous access event rather than merely a failed attempt. Other flagged accounts (such as jschott) show only failed login attempts from RU IP addresses, which indicate attack attempts but not confirmed unauthorized access. Since a successful login from a suspicious foreign region represents an active compromise, it takes priority for investigation over accounts with only failed attempts.
Community Discussion