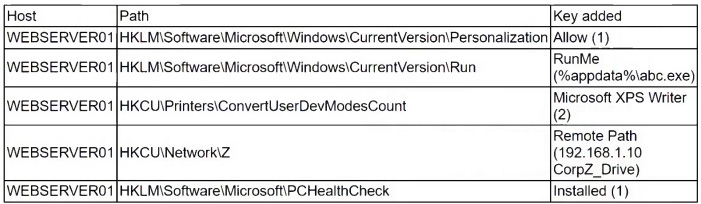
The FIM alert shows a value 'RunMe' pointing to %appdata%\abc.exe added under HKLM\Software\Microsoft\Windows\CurrentVersion\Run. The Run key is the classic autostart location, so any executable referenced there launches automatically at startup - a textbook persistence technique (MITRE ATT&CK T1547.001), and running from the user's AppData folder is a strong malware indicator. The mapped network drive under HKCU\Network\Z (option B) is normal drive-mapping behavior and does not by itself indicate exfiltration, the Personalization and printer keys are benign, and nothing in the alert touches firewall settings (D). Thus the best description is that a new program has been set to execute on system start.
Community Discussion