QuestionQ26
VerifiedSecurity OperationsA company finds that its proprietary information is being sold on the dark web. A security analyst uses threat hunting to look for indicators of compromise. After using a network packet-capture tool, the analyst identifies millions of packets resembling the following:
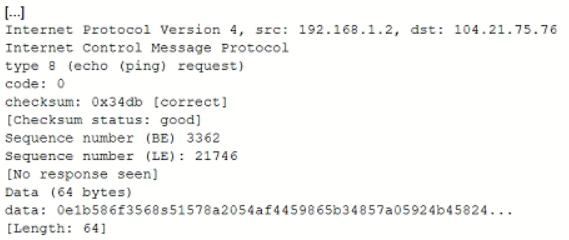
The analyst finds no other abnormalities. Which of the following is the most likely malicious activity in this scenario?
Community Discussion