QuestionQ24
Incident Response and ManagementThe SOC team restores a user's access after a threat actor successfully carried out a business account compromise in which the attacker revoked the legitimate user’s access. The following logs are supplied to a SOC analyst:
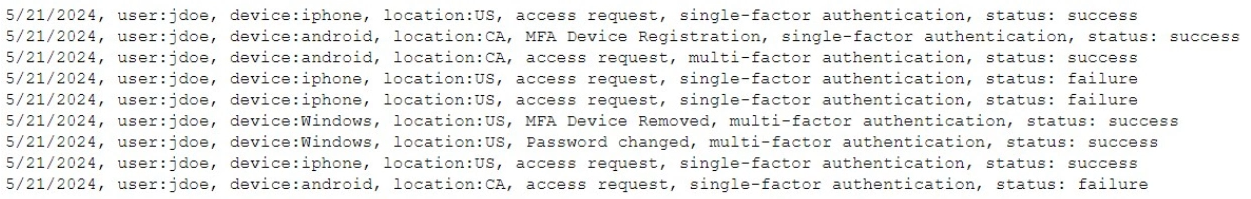
Which of the following did the threat actor most likely use during the compromise?
Community Discussion