QuestionQ75

VerifiedSecurity Engineering

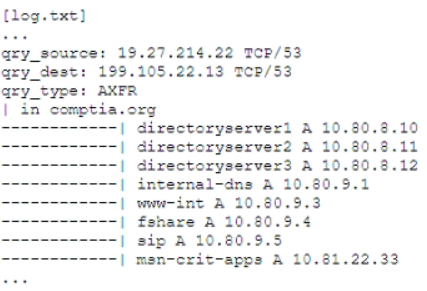
A senior security engineer flags the following log file snippet as having likely facilitated an attacker's lateral movement in a recent breach:
Question Image

Which of the following solutions, if implemented, would mitigate the risk of this issue reoccurring?

Explanation

The log shows an external host performing a full zone transfer (AXFR) against the internal DNS server, dumping internal hostnames and IP addresses for directory servers, internal DNS, file shares, and mission-critical apps, information an attacker used to move laterally. Restricting or disabling zone transfers to authorized secondary DNS servers only prevents this wholesale disclosure of internal network topology, while masking, UDP-only restrictions, or client-source filtering do not address the underlying AXFR exposure.

Community Discussion

No comments yet. Be the first to start the discussion!