QuestionQ61

VerifiedSecurity Operations

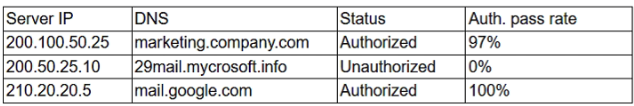
A security engineer discovers that some legacy systems are still in use or were not properly decommissioned. After further investigation, the engineer identifies that an unknown and potentially malicious server is also sending emails on behalf of the company.

The security engineer extracts the following data for review:
Question Image

Which of the following actions should the security engineer take next?

Choose two
Explanation

Moving the DMARC policy to reject enforces that spoofed or unaligned mail is rejected outright rather than merely flagged, and changing SPF to a hard fail (-all) makes messages from servers not listed in the SPF record explicitly fail authentication instead of being accepted or soft-failed. Rotating the DKIM selector does not address an unauthorized sending server since DKIM key compromise was not indicated, and adjusting the MX record only affects inbound mail routing, not who is authorized to send as the domain. Learn more: DMARC Overview (dmarc.org)

Community Discussion

No comments yet. Be the first to start the discussion!