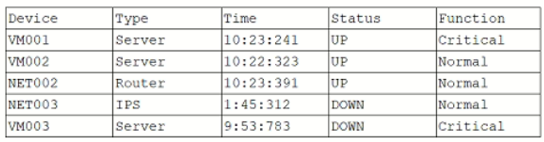
A company SIEM collects information about the log sources. Given the following report information:
Which of the following actions should a security engineer take to enhance the security monitoring posture?
The report shows two log sources, an IPS and a critical server, in a DOWN status, meaning the SIEM is currently blind to events from those systems; the priority action is to assess and remediate these non-reporting devices so their logs are collected again. Timing calibration, use-case libraries, and resiliency planning are useful monitoring improvements but do not address the immediate gap of devices that have stopped sending logs entirely.
Community Discussion