QuestionQ43

Security Engineering

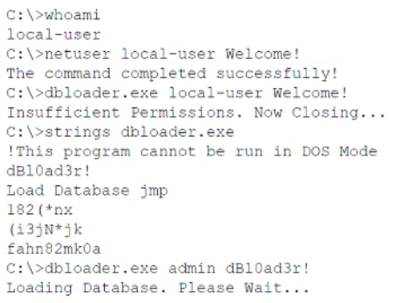
Recent reports indicate that a software tool is being exploited. Attackers were able to bypass user access controls and load a database. A security analyst needs to find the vulnerability and recommend a mitigation. The analyst generates the following output:

Question Image

Which of the following would the analyst most likely recommend?

Explanation

The captured console output shows an analyst running strings against dbloader.exe and finding the plaintext password "dBl0ad3r!" embedded in the binary, which the attacker then used to authenticate as admin and bypass the intended access control check. Hard-coded credentials in compiled code are a classic finding that strings/reverse-engineering can expose, so the fix is to remove them from the source and use a secure secrets-management mechanism instead. EDR, fuzz testing, and password-change restrictions do not address the root cause of a credential baked into the application itself.

Community Discussion

No comments yet. Be the first to start the discussion!