QuestionQ40

Security Engineering

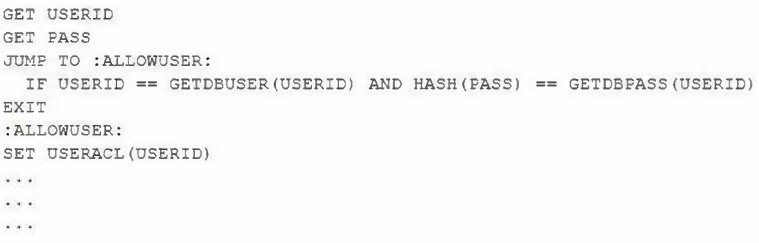
A programmer is reviewing the following proprietary piece of code that was identified as a vulnerability due to users being authenticated when they provide incorrect credentials:

Question Image

Which of the following should the programmer implement to remediate the code vulnerability?

Explanation

The routine reads the user ID and password but then executes an unconditional jump straight to the :ALLOWUSER label, so the credential comparison that follows it is never actually reached before access is granted. Making the credential check and the access-granting logic execute as a single atomic operation prevents this kind of control-flow bypass, whereas the input is already validated by the hash comparison, there is no time-of-check/time-of-use gap involved, and the flaw exists regardless of whether the database connection is encrypted.

Community Discussion

No comments yet. Be the first to start the discussion!