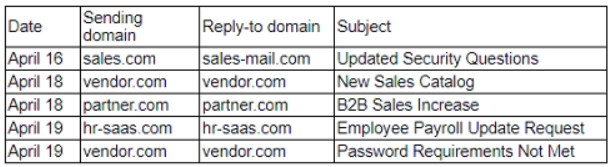
A security analyst needs to ensure email domains that send phishing attempts without previous communications are not delivered to mailboxes. The following email headers are being reviewed:
Which of the following is the best action for the security analyst to take?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion