QuestionQ15

Security Operations

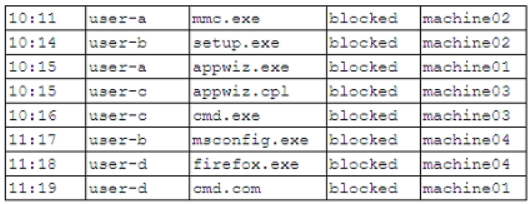
A company's internal network is experiencing a security breach and the threat actor is still active Due to business requirements, users in this environment are allowed to utilize multiple machines at the same time. Given the following log snippet:

Question Image

Which of the following accounts should a security analyst disable to best contain the incident without impacting valid users?

Explanation

User-d demonstrates the strongest indicator of compromise: accessing two different machines (firefox.exe on machine04, cmd.com on machine01) within a 1-minute window. This rapid multi-system access pattern indicates automated lateral movement or threat actor activity, requiring immediate containment. Users A, B, and C show only single-machine or limited tool usage patterns, making user-d the highest-risk account to disable.

Community Discussion

No comments yet. Be the first to start the discussion!