300-730 SVPN: Implementing Secure Solutions with Virtual Private Networks
By Cisco · Question Mode
QuestionQ13
Troubleshooting using ASDM and CLI
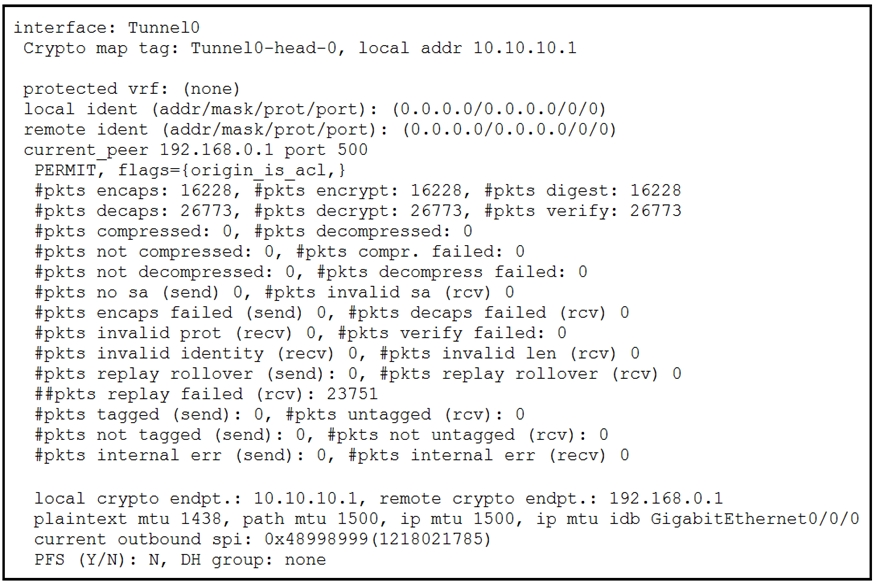
Refer to the exhibit. After a tunnel is configured between two sites, users report that connections to applications across the VPN do not work consistently.
The output from show crypto ipsec sa was captured on one of the VPN devices. Based on this output, what should be done to resolve the issue?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion