QuestionQ80

VerifiedPolicy Enforcement
Question Image

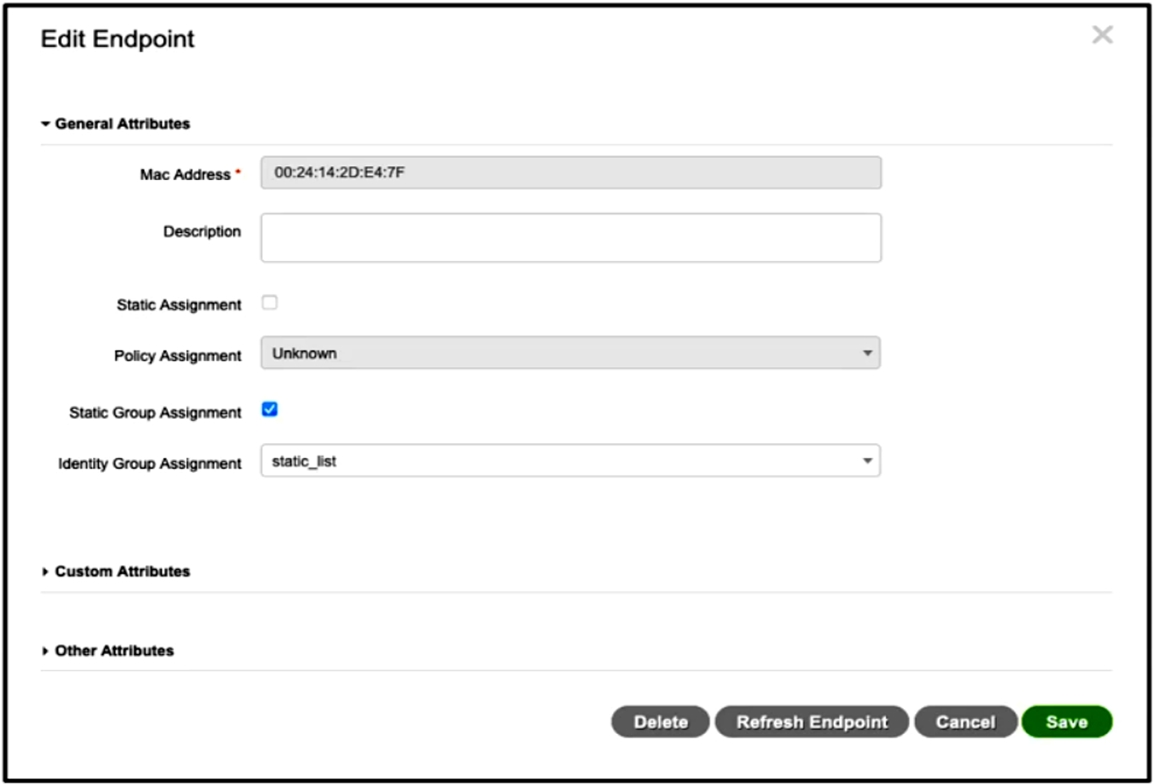
Refer to the exhibit. An administrator manually adds a device to a Cisco ISE identity group so that it can access the network when needed without authentication. During testing, the administrator observes that the device never reaches the correct authorization policy line with the condition EndPoints-LogicalProfile EQUALS static_list. Why does this occur?

Explanation

static_list is statically assigned as an endpoint identity group, whereas EndPoints-LogicalProfile evaluates the endpoint’s logical-profile membership. With the endpoint policy still set to Unknown, no logical profile named static_list is assigned, so that authorization condition does not match. Cisco ISE treats the Policy Assignment and Identity Group Assignment fields as separate assignments.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!