QuestionQ88

VerifiedConfiguration
Question Image

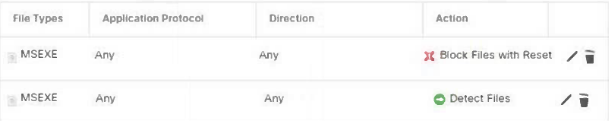
Refer to the exhibit. An engineer is configuring access-control rules on a Cisco Secure Firewall Threat Defense device. The access-control rules must include a file policy whose rules trigger when MSEXE files are accessed. Which two actions must be configured in the access rule?

Choose two
Explanation

Cisco Secure Firewall can associate a file policy with an access-control rule using the Allow or Interactive Block action. These actions permit the traffic to undergo file inspection; Trust and Monitor do not provide this file-policy inspection, while Block Files with Reset is configured inside the file policy rather than as the access-control rule action.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!