QuestionQ47

VerifiedManagement and Troubleshooting
Question Image

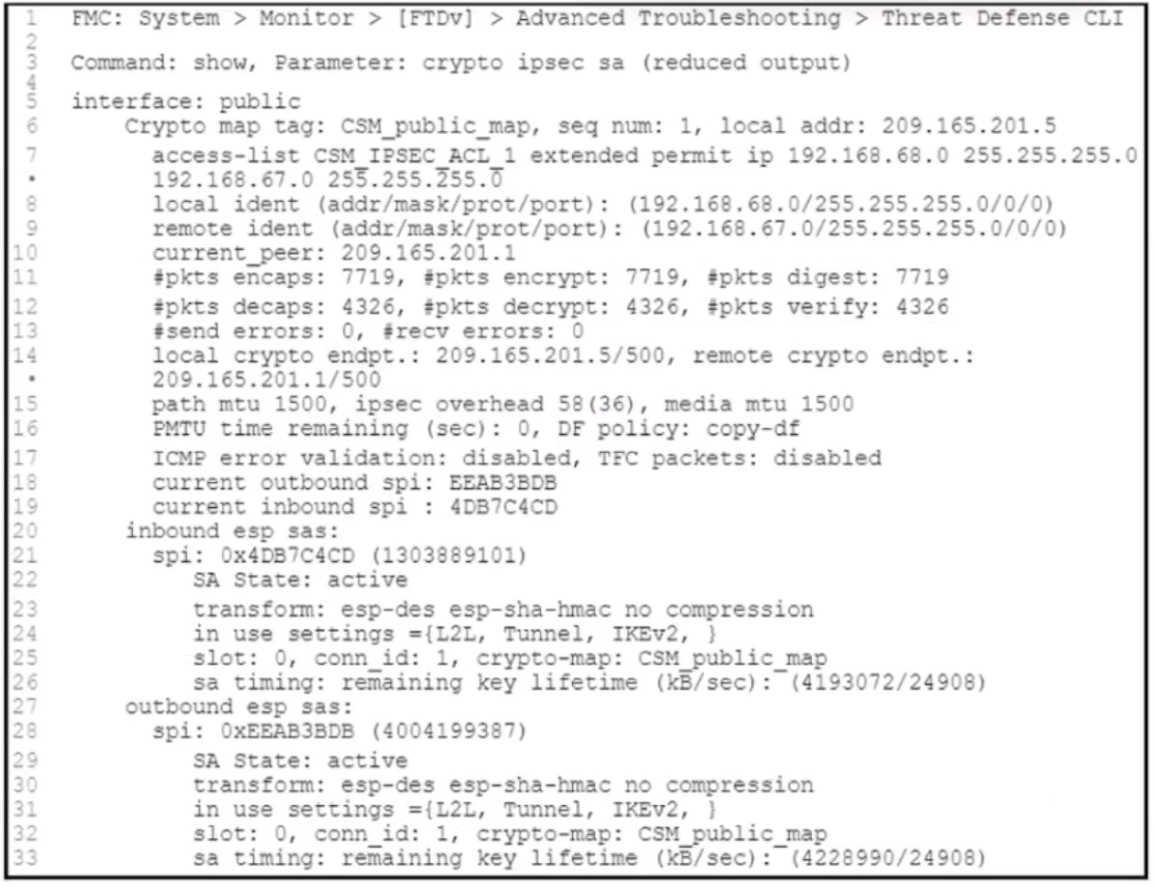
Refer to the exhibit. An engineer is troubleshooting VPN-tunnel connectivity problems. Users on the 192.168.68.0/24 network report that they cannot connect to a remote web server with IP address 192.168.67.100. The engineer verifies that NAT and access-control rules on the local Cisco Secure Firewall Threat Defense Virtual permit the connection. Which two configuration changes must the engineer make to resolve the connectivity issues?

Choose two
Explanation

An active IPsec SA does not ensure that the desired protected traffic matches on both VPN peers. The crypto access control lists (traffic selectors) must mirror one another for 192.168.68.0/24 and 192.168.67.0/24; an incorrect crypto ACL can prevent traffic from being sent through the tunnel or allow it only in one direction. The remote firewall must also permit the web connection and its return traffic. Cisco documents that incorrect crypto ACLs can cause traffic to flow in only one direction or not traverse the VPN at all.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!