QuestionQ71
VerifiedACI Packet ForwardingRefer to the exhibit.
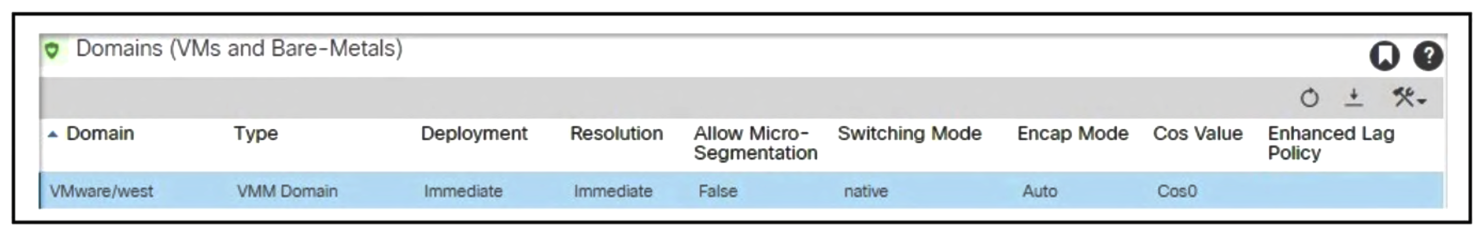
Malware is detected on endpoints in EPG-1001, so the infected endpoints must be isolated. The EPG has been configured for intra-EPG isolation and is associated with the VMware/west VMM Domain. However, endpoints are observed in the uSeg EPG.
Which set of actions completes the configuration?
Community Discussion