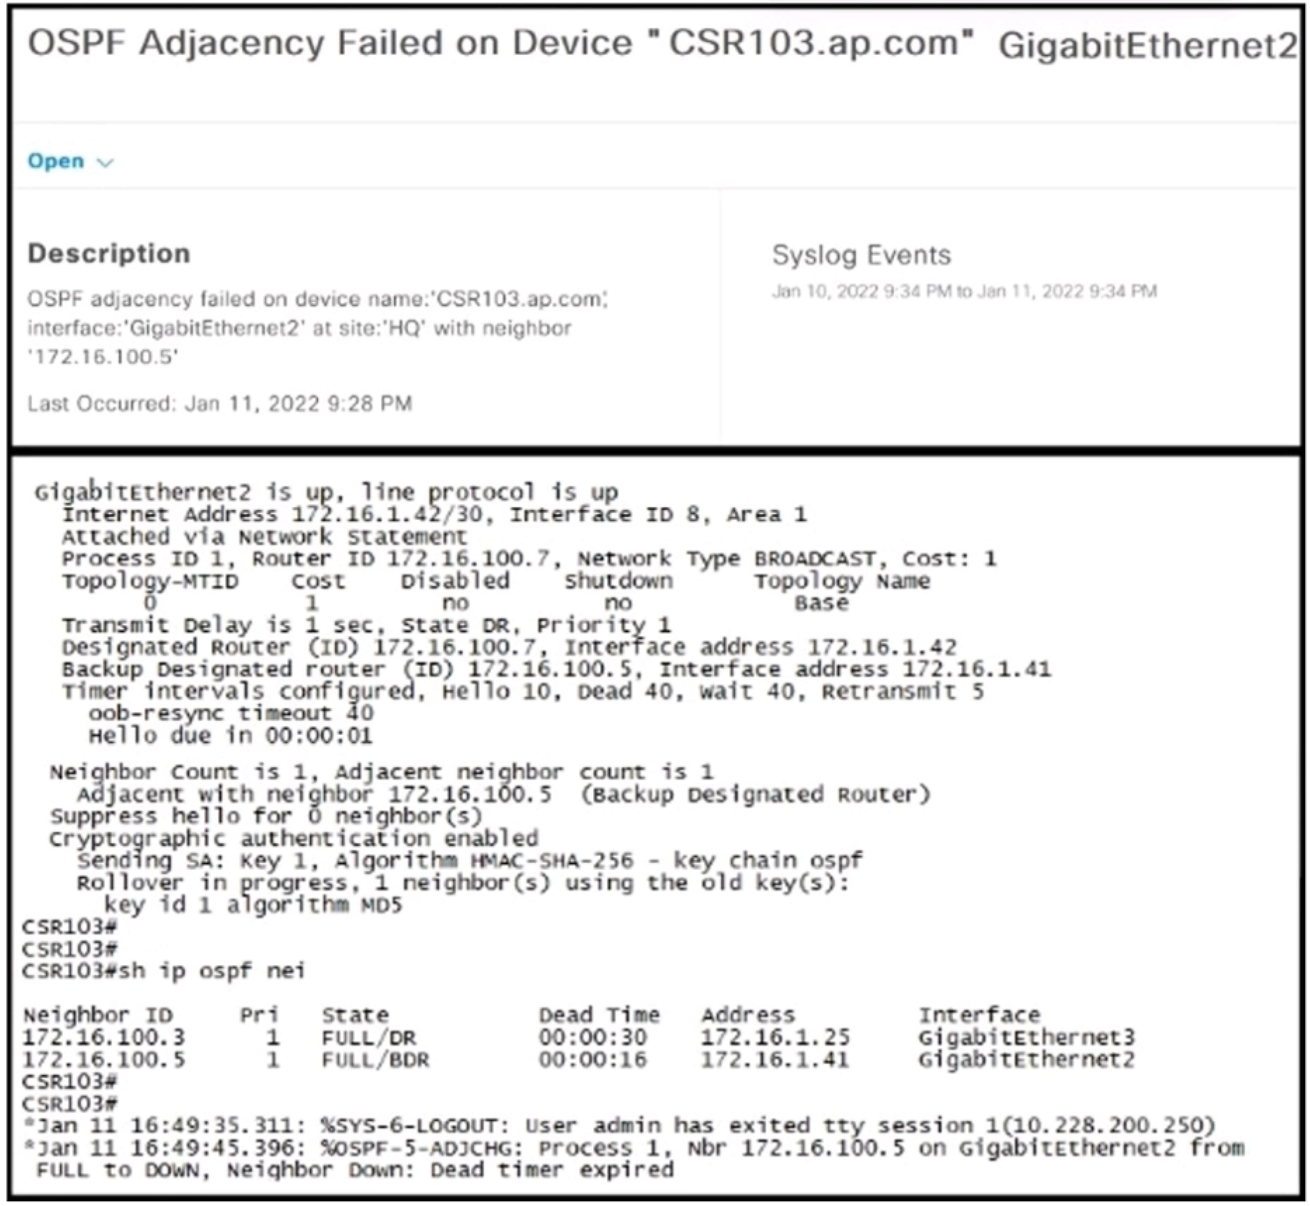
The adjacent router authenticates OSPF with MD5 using key ID 1, whereas the local interface is configured for key-chain HMAC-SHA-256 authentication. Configuring ip ospf message-digest-key 1 md5 cisco together with ip ospf authentication message-digest on the interface makes the authentication method, key ID, and secret match. When an OSPF interface is configured to use a key chain, previously configured MD5 message-digest keys are ignored; moreover, interface-level authentication overrides area-level authentication.
Community Discussion