QuestionQ88
VerifiedForensics Techniques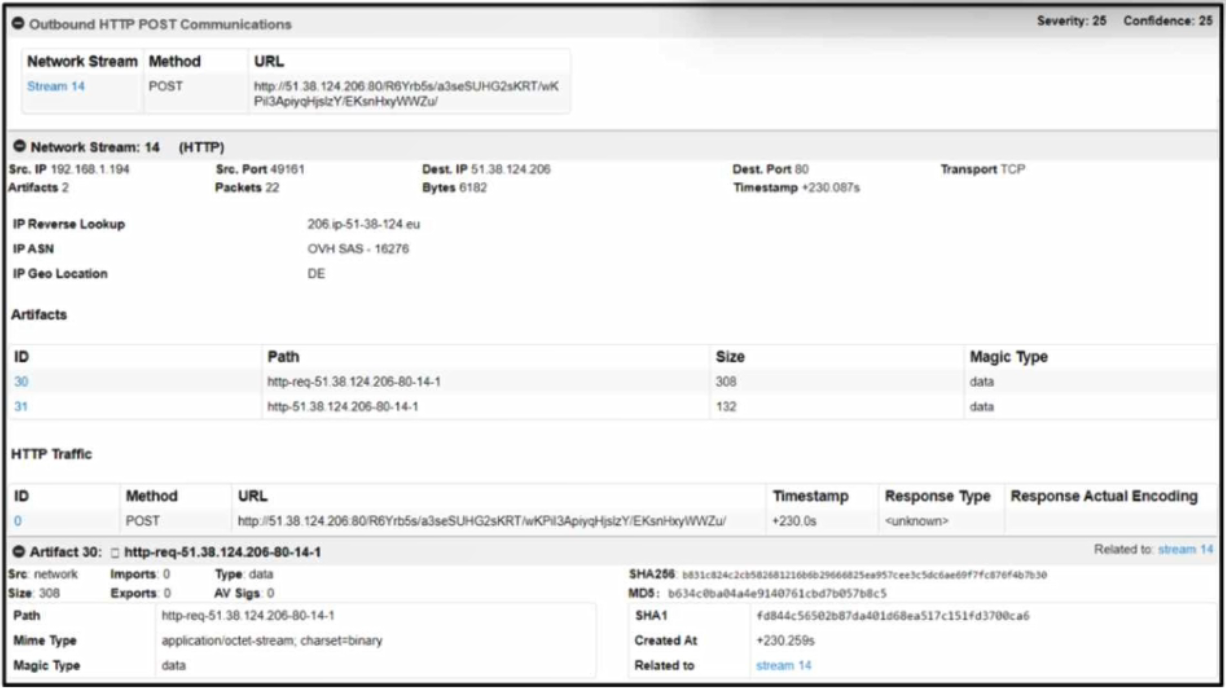
Refer to the exhibit. A suspicious binary was run and a Cisco Secure Malware Analytics report was generated. What do the artifacts indicate?
Refer to the exhibit. A suspicious binary was run and a Cisco Secure Malware Analytics report was generated. What do the artifacts indicate?
Community Discussion