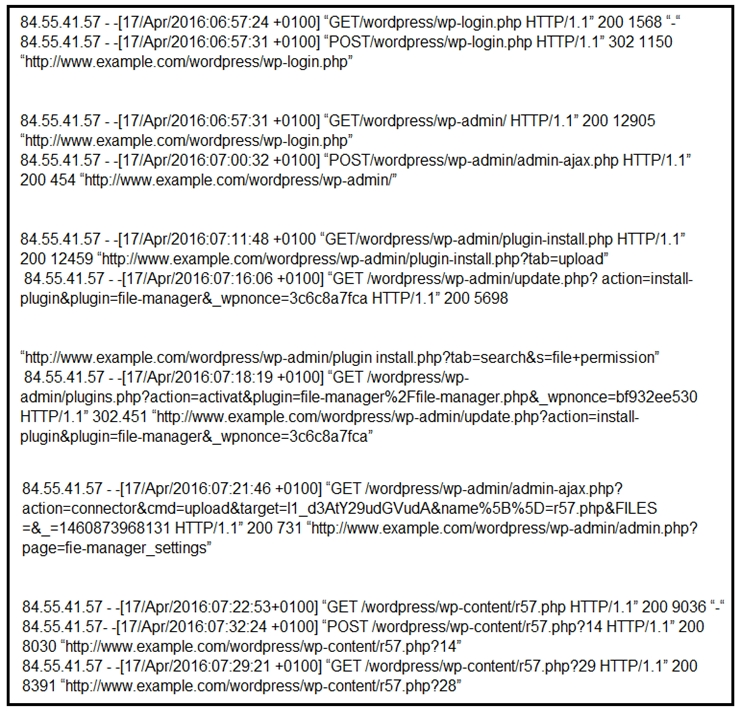
Refer to the exhibit. Which two conclusions should be made about the attack from the Apache access logs?
The access sequence records a successful WordPress login followed by installation and activation of the File Manager plugin. Requests to wp-content/r57.php afterward indicate that r57.php was uploaded through that plugin and accessed. The successful authentication and access to wp-admin show normal login to the WordPress administrative area.
wp-content/r57.php
r57.php
wp-admin
Community Discussion