QuestionQ56
VerifiedForensics Techniques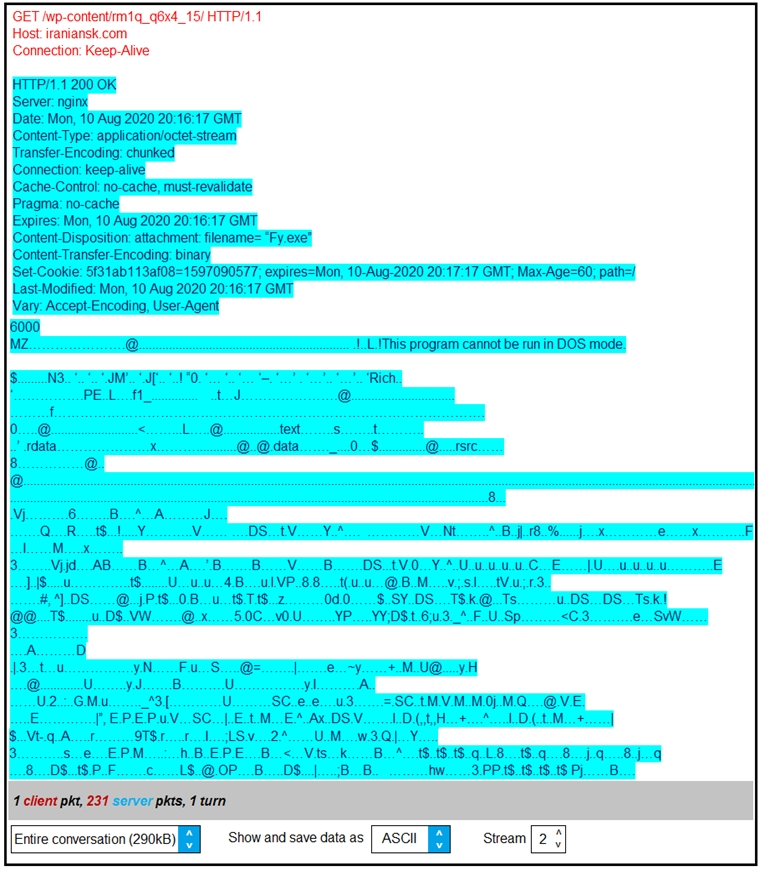
Refer to the exhibit. Based on the Wireshark output, which two indicators of compromise can be used to detect an Emotet malware download?
Choose two
Refer to the exhibit. Based on the Wireshark output, which two indicators of compromise can be used to detect an Emotet malware download?
Community Discussion