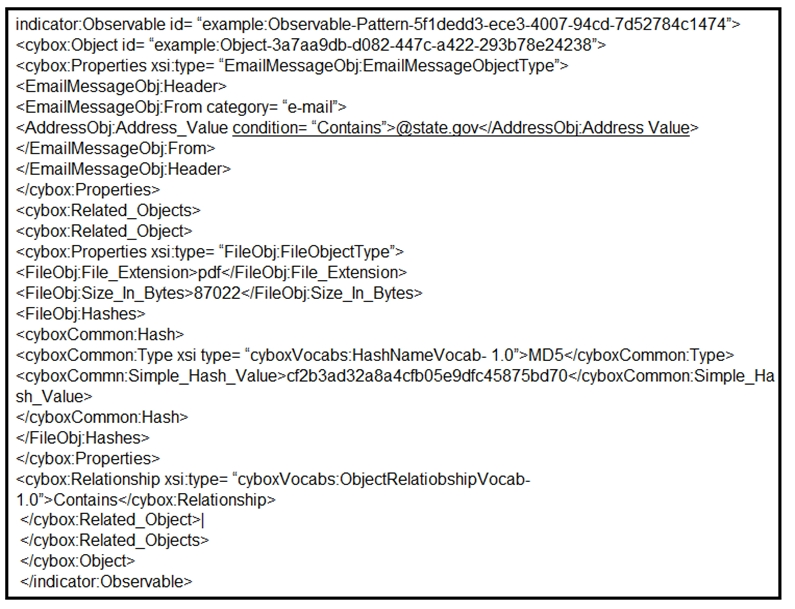
Refer to the exhibit. Which two actions should be performed based on this information?
A known malicious file hash can be added to antivirus or endpoint controls to prevent execution of that exact file. Email filtering can also block messages matching the identified sender pattern together with a PDF attachment having the specified MD5 hash. The observable does not support blanket blocking of all @state.gov senders or all PDF attachments.
@state.gov
Community Discussion