300-215 CBRFIR: Conducting Forensic Analysis and Incident Response Using Cisco Technologies for Cybersecurity
By Cisco · Question Mode
QuestionQ10
Forensics Techniques
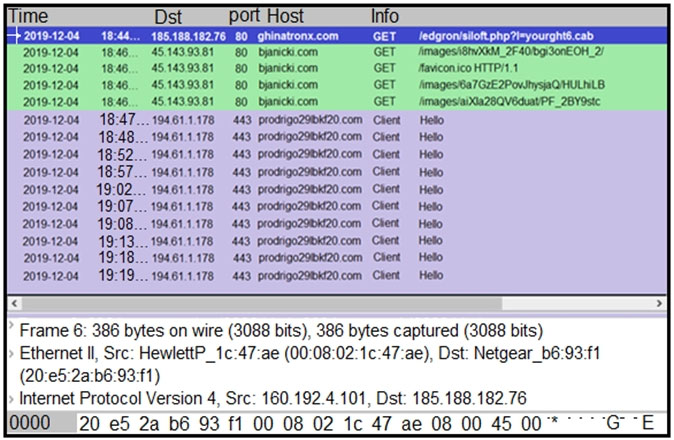
Refer to the exhibit. A network engineer is reviewing a Wireshark capture to identify the HTTP request that triggered download of the initial Ursnif banking Trojan binary. Which filter did the engineer use to sort the Wireshark traffic logs?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion