QuestionQ6

Device Hardening

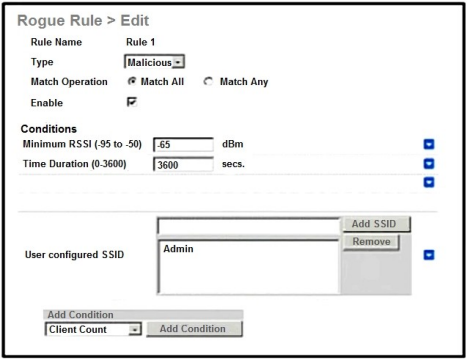
Refer to the exhibit.

Question Image

An engineer is attempting to manage rogues on the Cisco WLC. Based on the configuration, which AP is classified as malicious by the controller?

Explanation

The enabled malicious rule uses Match All, so a rogue AP must meet every configured condition: it must advertise the user-configured SSID Admin, be detected for at least 3,600 seconds, and have an RSSI greater than the -65 dBm threshold. An AP advertising Admin, seen for 4,000 seconds, at -60 dBm satisfies all three conditions and is therefore classified as malicious. The -70 dBm alternative does not meet the minimum RSSI requirement because it is weaker than -65 dBm.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!