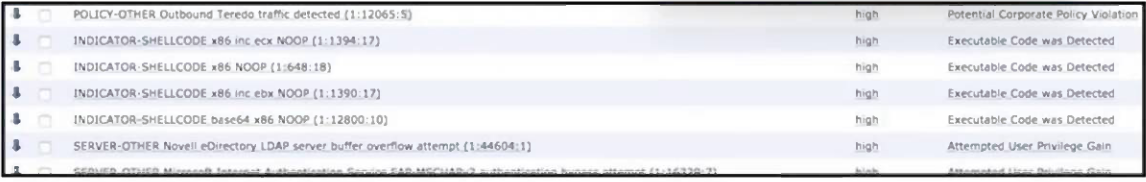
QuestionQ28Verified/Host-Based AnalysisCopy linkReport a problemAsk AstroTutorSave question Refer to the exhibit. What logical source device generated these events?Aproxy serverBIDS/IPSCNetFlow collectorDweb serverShow AnswerAnswerExplanationSnort intrusion events include signature messages with Generator ID, Snort ID, and revision in the (GID:SID:revision) format. Shellcode and policy signatures are produced by an intrusion detection or prevention engine that inspects network traffic, so the logical device is an IDS/IPS.Learn moreCisco Secure Firewall Management Center Administration Guide — Intrusion EventsCisco Secure Firewall Threat Defense — Intrusion PoliciesShow comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion