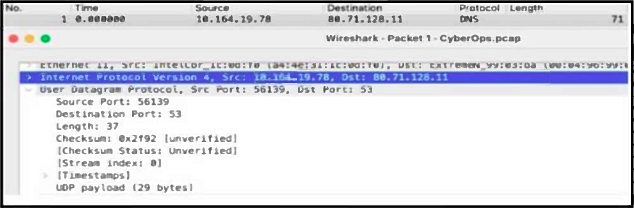
QuestionQ1Verified/Network Intrusion AnalysisCopy linkReport a problemAsk AstroTutorSave question Refer to the exhibit. What type of activity is occurring in the network?ADNS redirect attackBUDP floodCDNS floodDTCP reset attackShow AnswerAnswerExplanationDNS uses UDP port 53 for typical queries. UDP traffic directed to destination port 53 and identified as DNS is consistent with a DNS flood, in which a target receives a high volume of DNS requests.Show comments0Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion