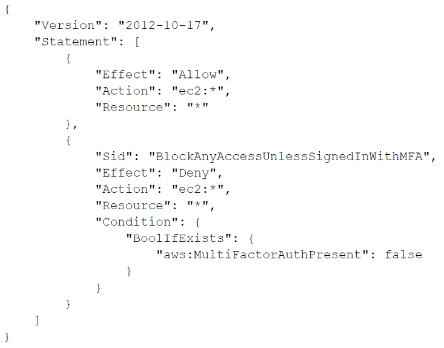
An AWS account administrator created an IAM group and attached the following managed policy to require every individual user to authenticate using multi-factor authentication:
After the policy was implemented, the administrator receives reports that users cannot perform Amazon EC2 commands through the AWS CLI.
What should the administrator do to resolve this issue while continuing to enforce multi-factor authentication?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion