QuestionQ9

VerifiedSecurity and Compliance

A company has an AWS Organizations organization. A DevOps engineer must manage multiple AWS accounts that are in different OUs in the organization. All resources within an account, including IAM policies and Amazon S3 policies, are deployed by using AWS CloudFormation. All templates and code are maintained in an AWS CodeCommit repository. Recently, some developers have been unable to access an S3 bucket from certain accounts in the organization.

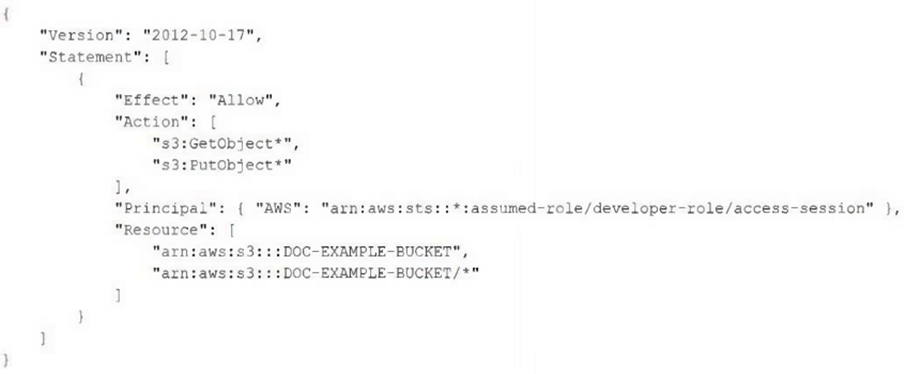
The following policy is attached to the S3 bucket:
Question Image

What should the DevOps engineer do to fix this access issue?

Explanation

The S3 bucket policy already grants the required object permissions to the specified developer-role sessions. An SCP attached at an affected account’s OU or inherited through the organization can limit permissions granted by an S3 bucket policy, and an applicable IAM permissions boundary can also deny the request. The effective permissions therefore require that both the SCP and permissions boundary permit the S3 actions. Managing the corrections in the CodeCommit repository and deploying them through CloudFormation preserves the stated infrastructure-as-code process.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!