QuestionQ38
VerifiedSecurity and ComplianceA company uses an AWS Organizations organization managed jointly by a security team and a DevOps team. Both teams access the accounts through AWS IAM Identity Center.
A separate group exists for each team. The DevOps team's group is assigned a permission set named DevOps. The permission set has the AdministratorAccess managed IAM policy attached and is applied to every account in the organization.
The security team needs to ensure that the DevOps team cannot access IAM Identity Center in the organization's management account. The security team attached the following SCP to the organization root:
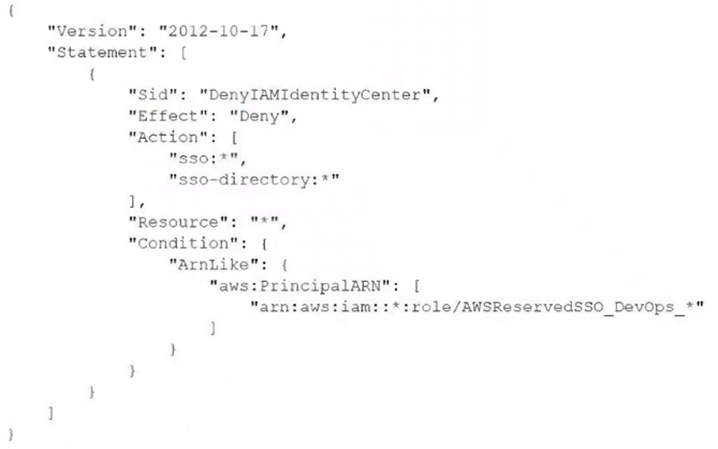
After the policy is implemented, the security team finds that the DevOps team can still access IAM Identity Center.
Which solution fixes the problem?
Community Discussion