QuestionQ22
VerifiedSecurity and ComplianceA company organizes its AWS accounts into OUs within an AWS Organizations organization. It has deployed a collection of Amazon API Gateway APIs in one Organizations account. The APIs are associated with that account’s VPC and currently have no authentication mechanism. Only principals in one specific OU must be permitted to invoke the APIs.
The company applies the following policy to the API Gateway interface VPC endpoint:
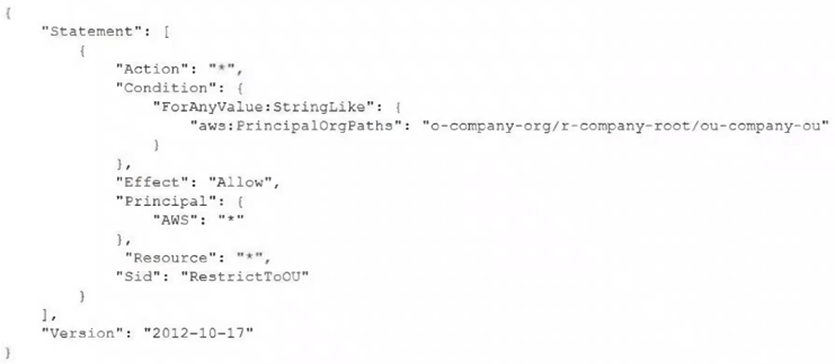
The company also modifies the API Gateway resource policies to deny invocations that do not pass through the interface VPC endpoint. After these updates, attempts to invoke an API by using the interface VPC endpoint URL produce this error: "User: anonymous is not authorized."
Which combination of steps will resolve this issue?
Community Discussion