QuestionQ39
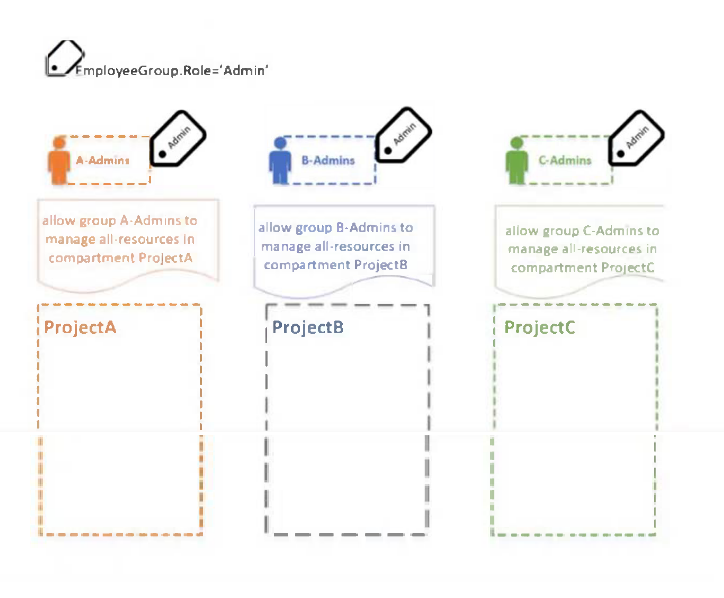
VerifiedIdentity and Access ManagementYou have three compartments: ProjectA, ProjectB, and ProjectC. An admin group exists for each compartment: A-Admins, B-Admins, and C-Admins.
Each admin group has full access to its corresponding compartment, as shown below.
Your organization has created the tag namespace EmployeeGroup.Role, and all admin groups are tagged with the value Admin.
You want to create a Test compartment that members of the three projects can share. You also need to grant admin access to all three existing admin groups.
Which policy would you write to accomplish this?
Community Discussion