QuestionQ74
VerifiedSection 3 – Configuring an NC2-on-AWS EnvironmentAn administrator has recently deployed an NC2 on AWS cluster in the North Virginia region, in availability zone us-east-1z. The cluster UUID is 0005F497-4962-91E4-4C9B-C4284D123835.
The cluster is consuming IPs from the 10.78.2.0/24 range.
The AWS VPC has the following available CIDR ranges:
10.78.0.0/1610.19.101.0/2410.0.0.0/22
The following subnets are configured in the NC2 AWS VPC:
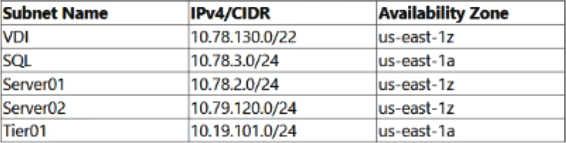
The following tags are applied to a Custom Network Security Group:
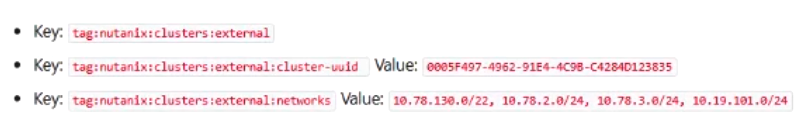
The Custom Network Security Group allows all inbound traffic from the 10.0.0.0/22 network.
Which two subnets can receive inbound traffic from AWS instances on a 10.0.0.0/22 network segment?
Choose two
Community Discussion