QuestionQ6
Deploy and manage AD DSOverview -
Contoso, Ltd. is a company with its main office in Seattle and two branch offices in Los Angeles and Montreal.
Existing Environment -
AD DS Environment -
The network has an on-premises Active Directory Domain Services (AD DS) forest named contoso.com. The forest includes two domains named contoso.com and canada.contoso.com.
The forest contains the domain controllers shown in the following table.
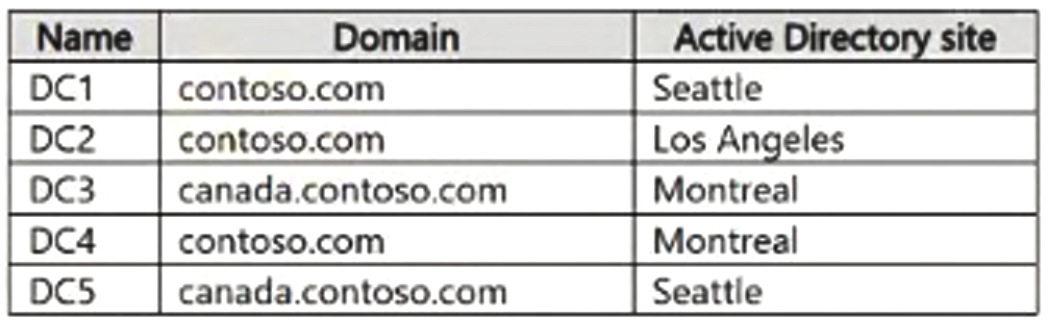
All domain controllers are global catalog servers.
Server Infrastructure -
The network includes the servers shown in the following table.
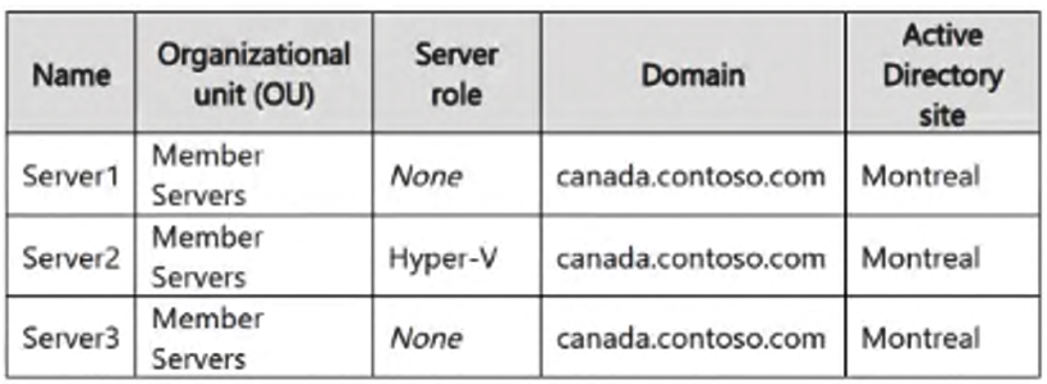
A server named Server4 runs Windows Server and is in a workgroup. Windows Defender Firewall on Server4 uses the private profile.
Server2 hosts three virtual machines named VM1, VM2, and VM3.
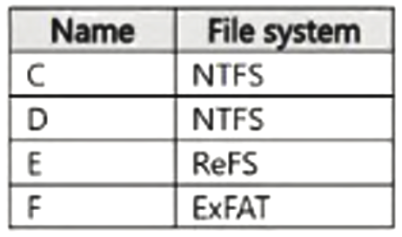
VM3 is a file server that stores data in the volumes shown in the following table.
Group Policies -
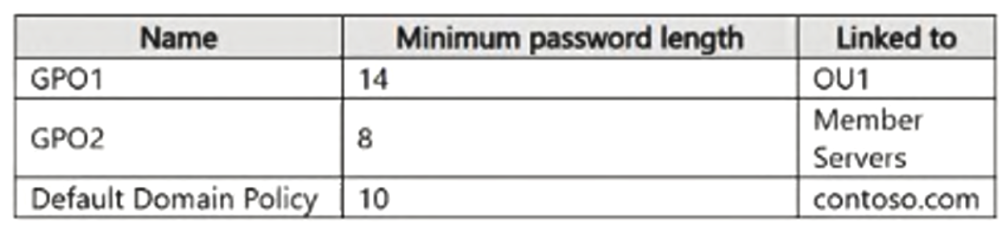
The contoso.com domain contains the Group Policies Objects (GPOs) shown in the following table.
Existing Identities -
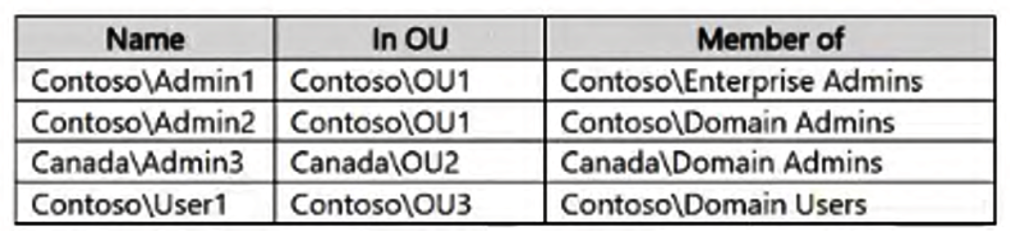
The forest includes the users shown in the following table.
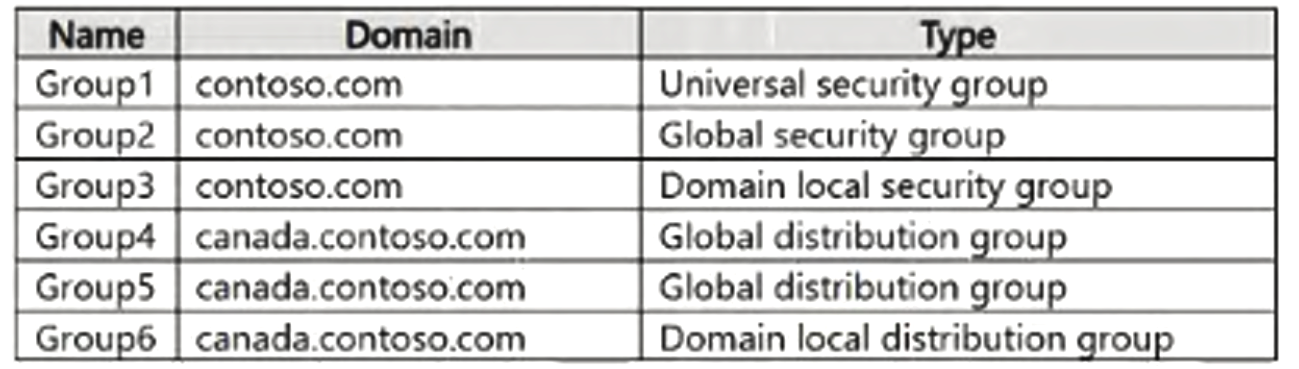
The forest includes the groups shown in the following table.
Current Problems -
When an administrator signs in to the console of VM2 by using Virtual Machine Connection and then disconnects from the session without signing out, another administrator can connect to that console session as the currently signed-in user.
Requirements -
Technical Requirements -
Contoso identifies the following technical requirements:
- Change the replication schedule for all site links to 30 minutes.
- Promote Server1 to a domain controller in canada.contoso.com.
- Install and authorize Server3 as a DHCP server.
- Ensure that User1 can manage the membership of all the groups in Contoso\OU3.
- Ensure that Server4 can be managed from Server1 by using PowerShell remoting.
- Ensure that virtual machines can run on VM1.
- Force users to provide credentials when they connect to VM2.
- On VM3, enable Data Deduplication on all volumes that support the feature.
You need to fulfill the technical requirements for User1. The solution must follow the principle of least privilege.
What should you do?
Community Discussion