QuestionQ145

VerifiedImplement Azure security

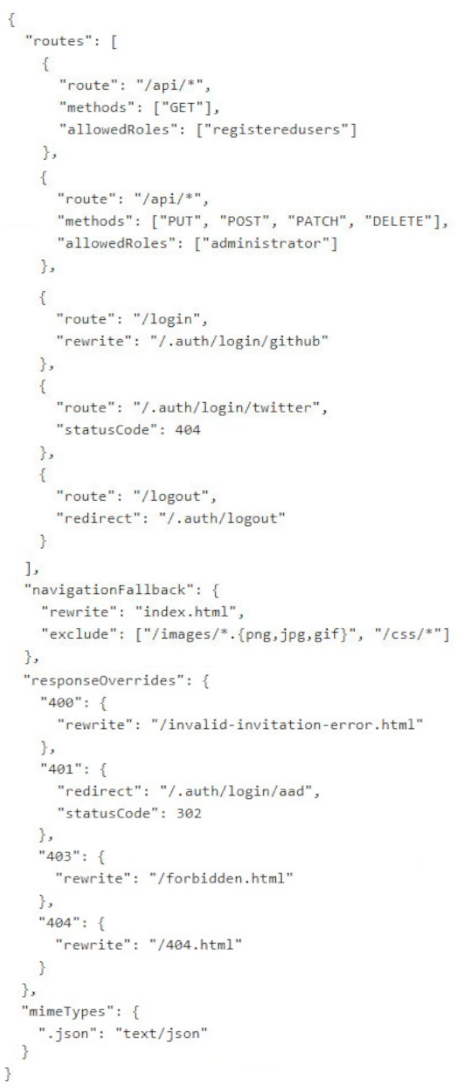
You develop and deploy the following staticwebapp.config.json file to the app_location specified in the workflow file for an Azure Static Web App:
Question Image

For each statement, select Yes if it is true. Otherwise, select No.

Yes or No
StatementsYesNo
Unauthenticated users are challenged to authenticate with GitHub.
A non-existent file in the /images/ folder will generate a 404 response code.
HTTP GET method requests from authenticated users in the role named registeredusers are sent to the API folder.
Authenticated users that are not in the role named registeredusers and unauthenticated users are served a 401 HTTP error when accessing the API folder.
Explanation

The responseOverrides for 401 redirect unauthorized requests to /.auth/login/aad (Azure AD), so unauthenticated users hitting a protected route are challenged with AAD, not GitHub; GitHub login only occurs if a user explicitly browses to /login (No). navigationFallback excludes /images/.{png,jpg,gif} from the index.html rewrite, so a missing image file is served directly and returns 404 (the 404 responseOverride rewrites to /404.html but a rewrite preserves the 404 status code) (Yes). The route /api/ with methods GET and allowedRoles registeredusers permits GET requests from registeredusers to reach the API (Yes). For statement 4, users lacking the registeredusers role and anonymous users would get a 401, but the 401 responseOverride converts that into a 302 redirect to the AAD login page, so they are NOT served a 401 error (No).

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!