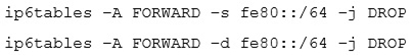
QuestionQ6Verified/System SecurityCopy linkReport a problemAsk AstroTutorSave questionWhich of the statements below are correct about these commands, executed on a Linux router? Choose twoAPackets with source or destination addresses from fe80::/64 will never occur in the FORWARD chainBThe rules disable packet forwarding because network nodes always use addresses from fe80::/64 to identify routers in their routing tablesCip6tables returns an error for the second command because the affected network is already part of another ruleDBoth ip6tables commands complete without an error message or warningEThe rules suppress any automatic configuration through router advertisements or DHCPv6Show AnswerAnswerExplanationThe fe80::/64 prefix is link-local IPv6 address space. Routers must not forward packets whose source or destination is link-local to another link, so those packets do not traverse the forwarding path. The two valid ip6tables -A FORWARD rules can coexist because ip6tables permits independently appended rules, including rules with overlapping match criteria.Learn moreRFC 4291: IPv6 Addressing Architectureiptables and ip6tables manualShow comments5Show commentsCommunity DiscussionNo comments yet. Be the first to start the discussion!
Community Discussion