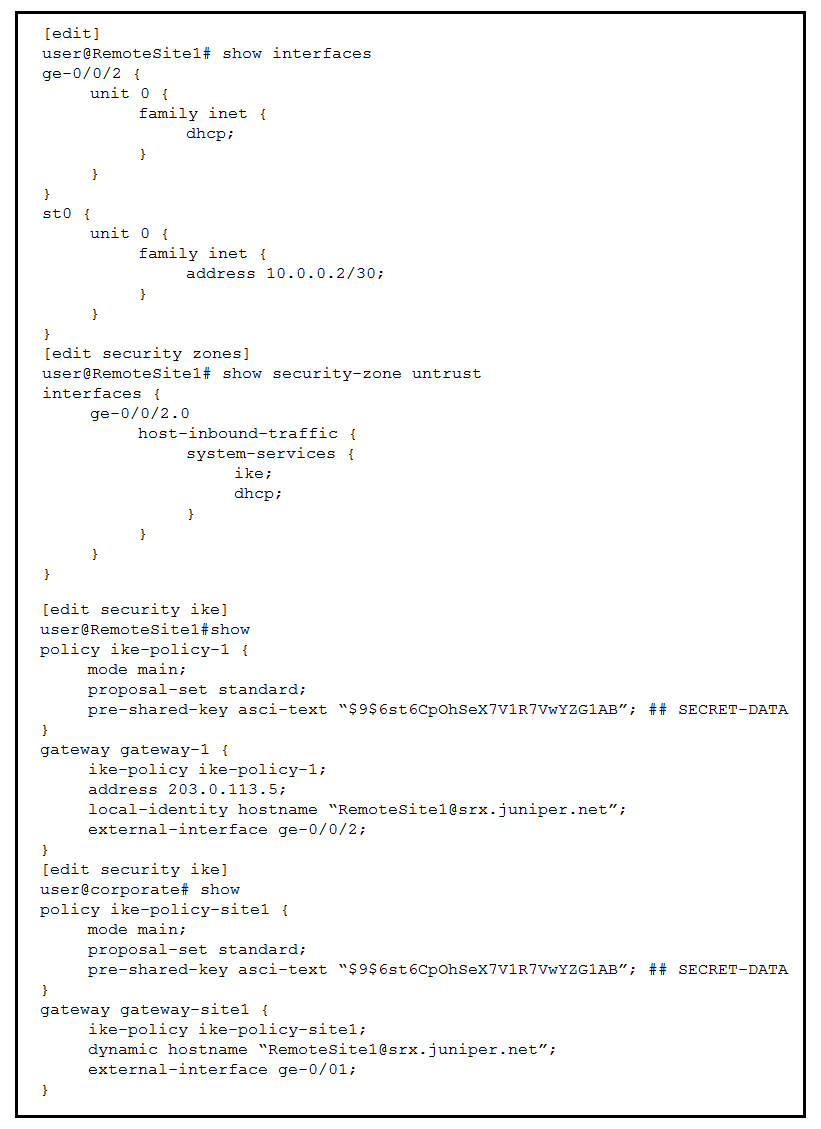
You are troubleshooting a newly configured IPsec VPN between your corporate office and the RemoteSite1 SRX Series device. The VPN is currently not establishing. The RemoteSite1 device receives an IP address for its gateway interface through DHCP.
Referring to the exhibit, which action will resolve this issue?
Community Discussion
No comments yet. Be the first to start the discussion!
Community Discussion