QuestionQ35

VerifiedNetwork Address Translation

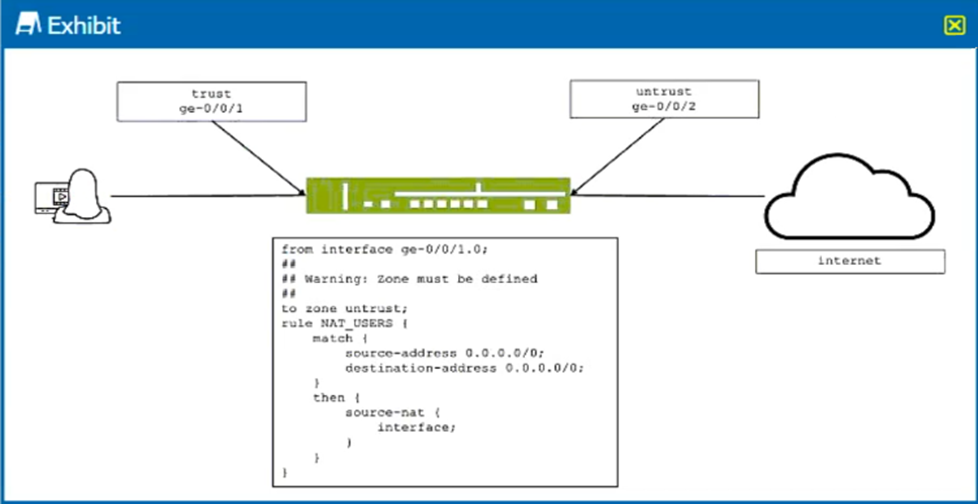
Click the Exhibit button.

Question Image

You are configuring an SRX firewall to perform NAT on user traffic destined for the Internet.

With reference to the exhibit, which configuration change will enable the NAT policy?

Explanation

A source NAT rule set uses both source and destination traffic-direction conditions. Internet-bound traffic exits through ge-0/0/2.0, so that interface must belong to the untrust security zone referenced by the rule set. Assigning ge-0/0/2.0 to untrust enables the rule’s destination-zone match and interface source NAT for that traffic.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!