QuestionQ105
VerifiedCampus Network Technology DetailsR1 and R2 establish an IPsec VPN in ISAKMP mode for communication, as shown below. IPsec proposals on R1 and R2 use ESP with tunnel encapsulation, SHA1 authentication, and AES-256 encryption. IKE peers use IKEv1, main mode for IKEv1 phase 1 negotiation, and PSK authentication with the PSK Huawei@123. IKE proposals use SHA1 authentication, AES-256 encryption, and DH group 1 for IKE negotiation. Based on these R1 and R2 settings, map the configuration items to their correct locations.
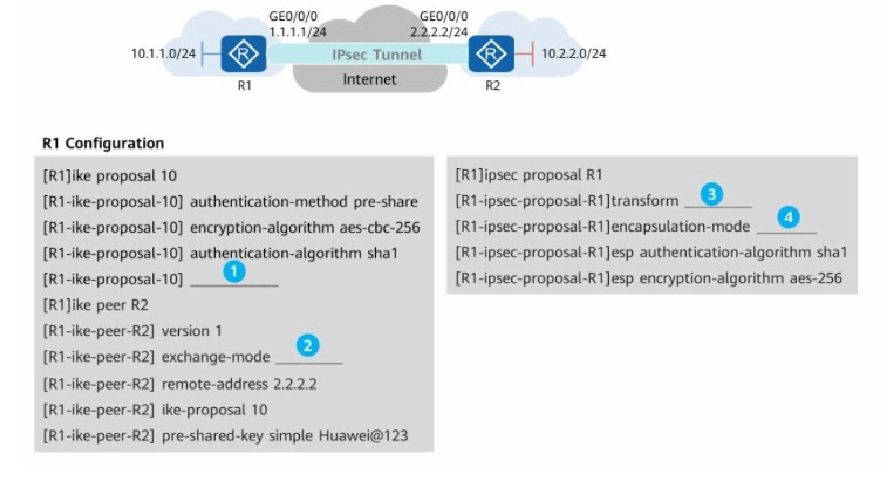
Drag & Drop
1
2
3
4
Community Discussion