QuestionQ57
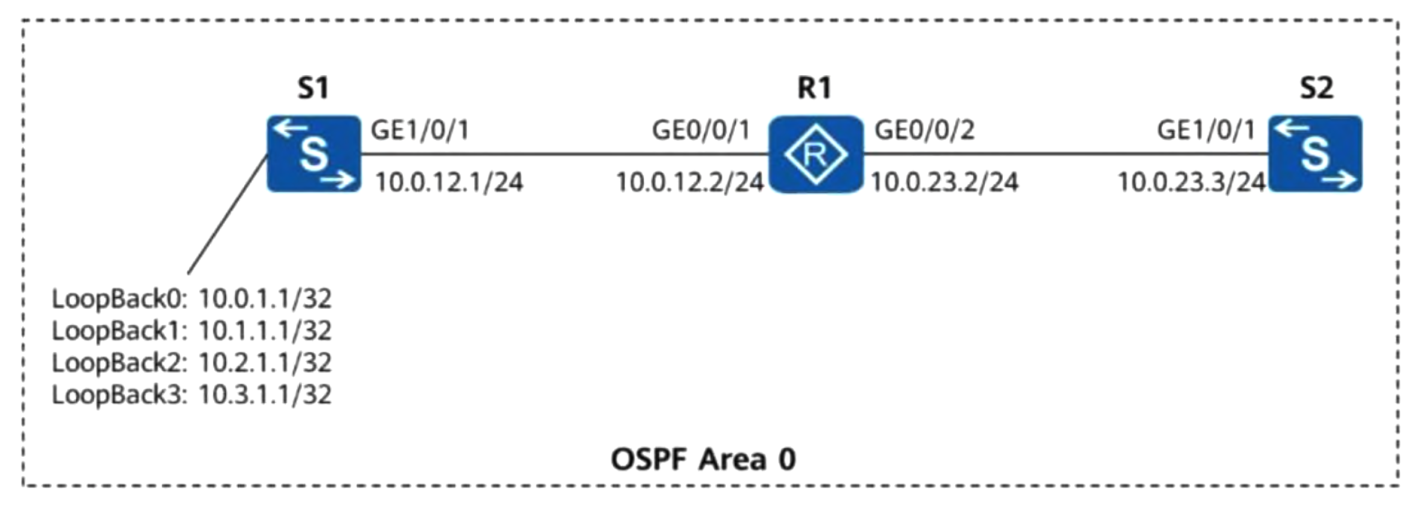
VerifiedCyber security infrastructure and network accessIn the OSPF network shown, all IP addresses can communicate with one another. The following configuration is then added on R1:
[R1] acl 3000
[R1-acl4-advance-3000] rule deny ip source 10.0.1.1 0.0.0.0
[R1-acl4-advance-3000] rule deny ip source 10.1.1.1 0.0.0.0
[R1-acl4-advance-3000] rule deny ip source 10.3.1.1 0.0.0.0
[R1-acl4-advance-3000] rule permit ip
[R1-acl4-advance-3000] quit
[R1] traffic classifier test
[R1-classifier-test] if-match acl 3000
[R1-classifier-test] quit
[R1] traffic behavior test
[R1-behavior-test] permit
[R1-behavior-test] quit
[R1] traffic policy test
[R1-trafficpolicy-test] classifier test behavior test
[R1-trafficpolicy-test] quit
[R1] interface GE 0/0/1
[R1-GE0/0/1] traffic-policy test inbound
[R1-GE0/0/1] quit
Which S1 IP address can successfully ping 10.0.23.3?
Community Discussion