QuestionQ58
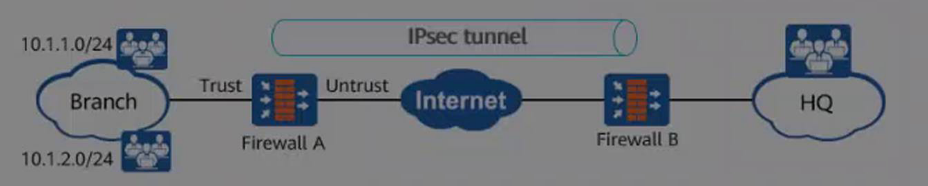
VerifiedNetwork SecurityAs illustrated, the firewall NAT policy is configured as follows:
[FW-policy-nat]display this
nat-policy
rule name no-nat
source-zone trust
destination-zone untrust
source-address 10.1.2.0 mask 255.255.255.0
action no-nat
rule name nat
source-zone trust
destination-zone untrust
action source-nat easy-ip
Assuming that all other configurations are correct, can the IPsec VPN service be accessed normally?
Community Discussion