QuestionQ6
VerifiedProtect and DefendIntroduction to the customer
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking network-infrastructure devices.
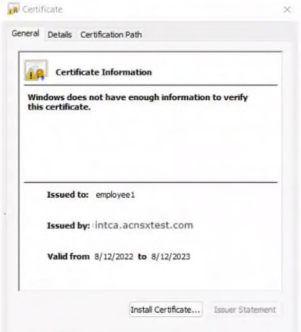
The company already has a Windows domain and Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers. An example certificate issued by the Windows CA is shown here.
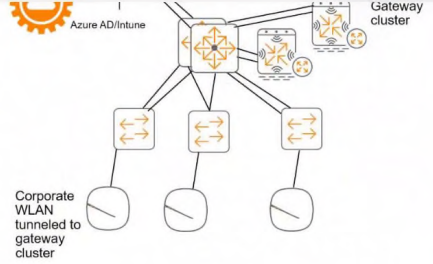
ClearPass cluster IP addressing and hostnames
A customer's ClearPass cluster has the following IP addresses:
- Publisher = 10.47.47.5
- Subscriber 1 = 10.47.47.6
- Subscriber 2 = 10.47.47.7
- Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
The customer's DNS server contains these entries:
- cp.acnsxtest.com = 10.47.47.5
- cps1.acnsxtest.com = 10.47.47.6
- cps2.acnsxtest.com = 10.47.47.7
- radius.acnsxtest.com = 10.47.47.8
- onboard.acnsxtest.com = 10.47.47.8
Refer to the scenario.
You created a role-mapping policy as displayed in the exhibits below.
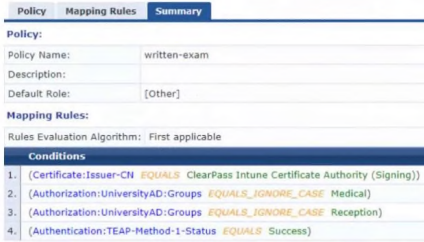
What one change must you make to this policy?
Community Discussion