QuestionQ19
VerifiedProtect and DefendRefer to the exhibit.
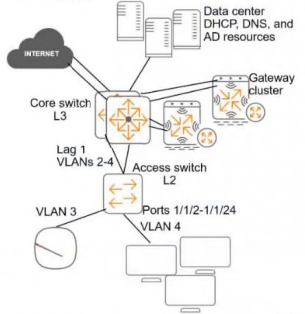
A customer needs protection from ARP poisoning in VLAN 4. The following lists all settings for VLAN 4 and the physical interfaces associated with VLAN 4 on the AOS-CX access-layer switch:
interface 1/1/2-1/1/24
 no shutdown
 no routing
 vlan access 4
 exit
interface lag 1
 no shutdown
 no routing
 vlan trunk native 1
 vlan trunk allowed 2-4
 arp inspection trust
 exit
vlan 4
 arp inspection
 exit
What is one problem with this configuration?
Community Discussion