QuestionQ13
VerifiedAnalyzeA hospital uses an AOS-10 architecture managed by HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways, with Security licenses, at each clinic. The gateways run IDS/IPS in IDS mode.
The Security Dashboard displays several recent events with the same signature, as shown below:
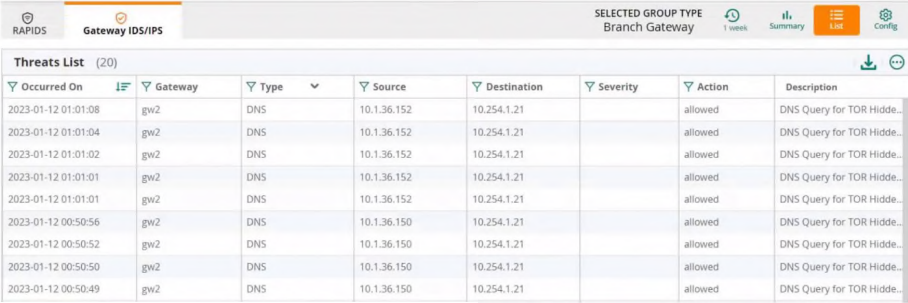
Refer to the scenario.
You want a record of the specific traffic that triggered the threat event. What should you do?
Community Discussion