QuestionQ38

Authentication/Authorization

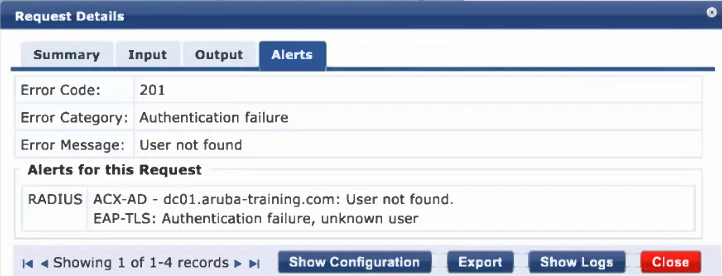
You configured a bridged-mode SSID using WPA3-Enterprise and EAP-TLS security. When an Active Directory-joined client with valid client certificates connects, HPE Aruba Networking ClearPass displays this error:

Question Image

What is required to resolve the issue?

Explanation

ClearPass Error Code 201 indicates that the requested identity was not found in the configured authentication source. With EAP-TLS, a successfully presented client certificate still requires ClearPass to locate the corresponding directory identity for policy processing. Adding the UPN to the ACX-AD authentication-source search lets ClearPass match the certificate identity to the Active Directory user and eliminates the unknown-user failure.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!