QuestionQ86
VerifiedSecure WLANRefer to the exhibit.
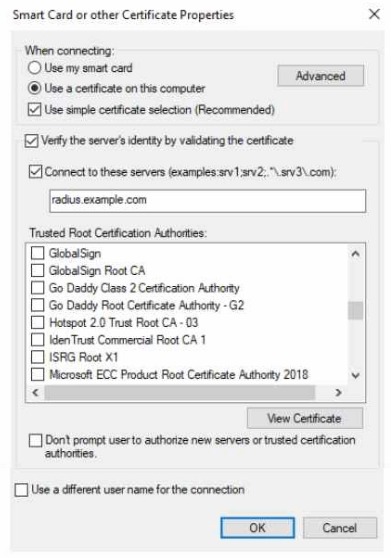
The exhibit displays the 802.1X-related settings for Windows domain clients. What should administrators change so that the settings follow security best practices?
Refer to the exhibit.
The exhibit displays the 802.1X-related settings for Windows domain clients. What should administrators change so that the settings follow security best practices?
Community Discussion