QuestionQ22

VerifiedProtect and Defend

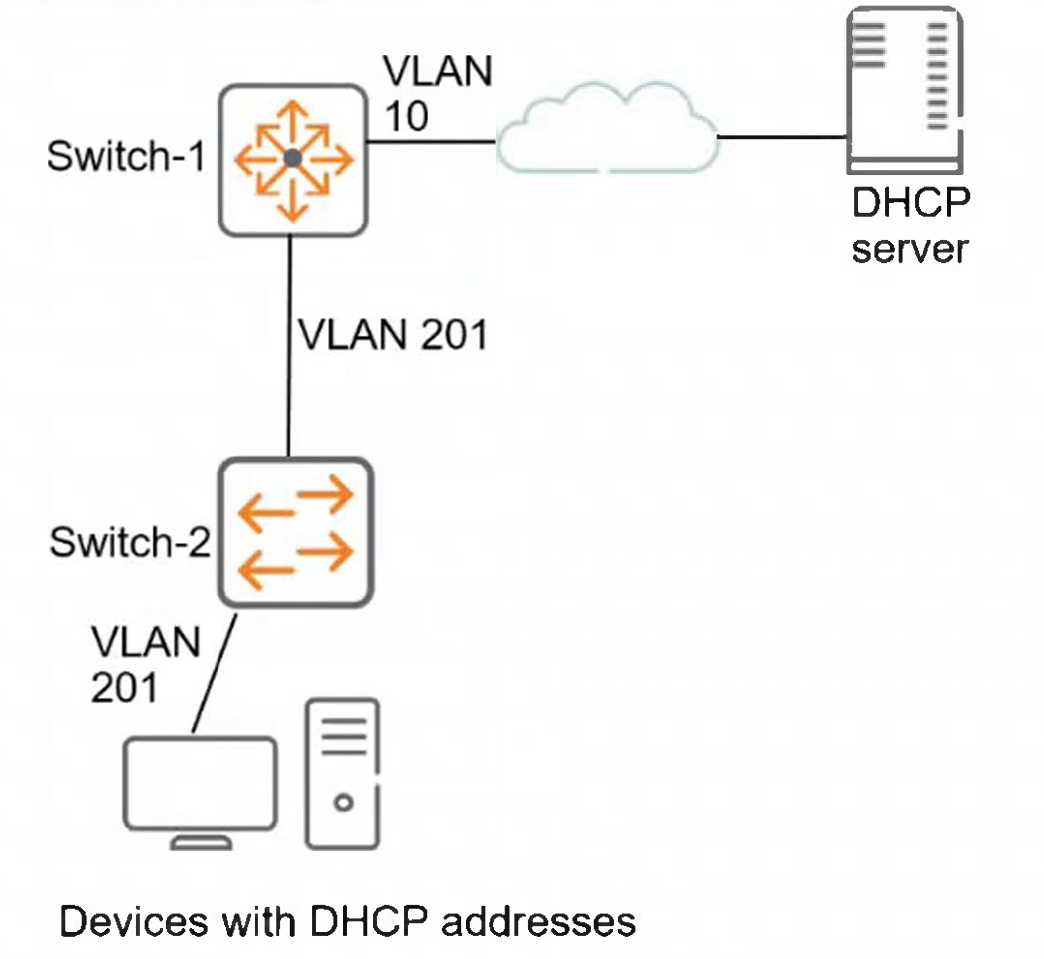
Refer to the exhibit.

Question Image

This company uses AOS-CX switches. The exhibit depicts one access-layer switch, Switch-2, as an example, although the campus contains additional switches.

The company wants to prevent internal users from exploiting ARP. Assume that DHCP snooping is already correctly configured in the environment.

What is the appropriate way to configure the switches to satisfy these requirements?

Explanation

Dynamic ARP Inspection is enabled on a per-VLAN basis and checks ARP received on untrusted ports against the DHCP snooping binding table. End-user ports should remain untrusted so forged ARP packets are rejected, while the uplink to Switch-1 is trusted to allow legitimate upstream ARP traffic. Thus, ARP inspection must be enabled for VLAN 201 on Switch-2 and its Switch-1 uplink must be trusted.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!