QuestionQ7

Malicious Code & Exploit Mitigation

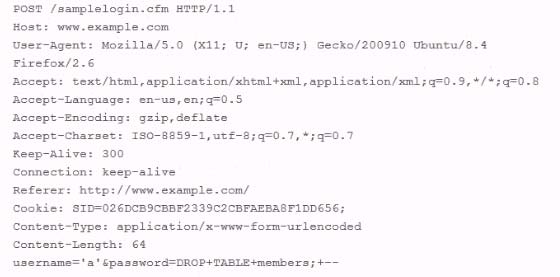
While using Wire shark to investigate user complaints that they cannot log in to a web application, you encounter an HTTP POST submitted through the application. The POST contents are shown below. Based on what is shown, which of the following would you recommend to prevent future damage to the database?

Question Image

Explanation

A malicious value that appends DROP TABLE members to a login field is a SQL-injection attempt that could execute destructive database commands if user input is incorporated into SQL unsafely. Sanitizing and validating user input prevents injection attacks; parameterized queries should also be used so supplied values are handled as data rather than executable SQL.

Learn more

Community Discussion

No comments yet. Be the first to start the discussion!