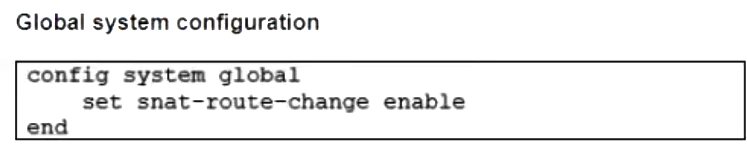
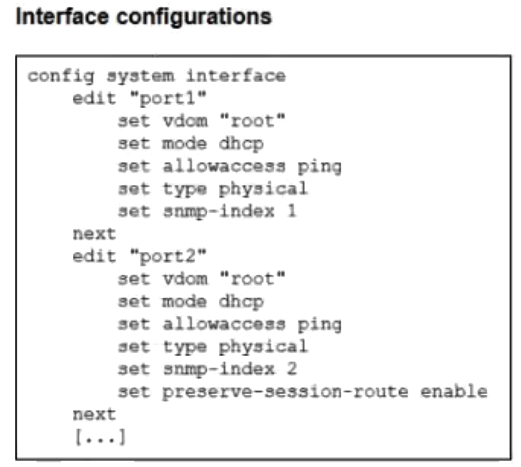
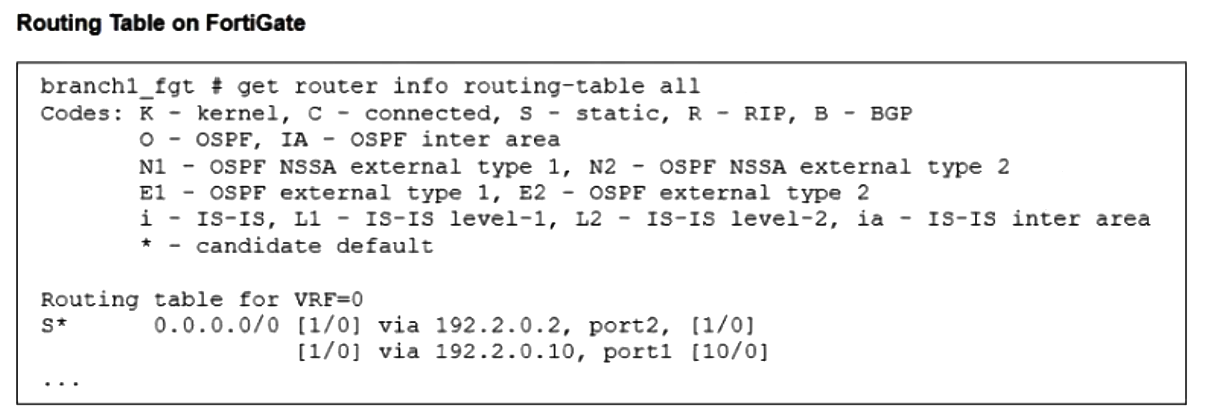
Raising the priority value on port2 to 20 makes the port1 default route (priority 10) preferred. The port2 route still remains in the routing table, so it stays valid. preserve-session-route is enabled on port2. FortiGate therefore marks sessions leaving port2 with the route_preserve flag, does not re-evaluate them after the routing change, and keeps them on port2 as long as their route is still valid. Fortinet documents that this option applies to both SNAT and non-SNAT sessions. Even with snat-route-change enabled, existing SNAT sessions on port2 are not moved to port1. Sessions are flagged dirty and re-evaluated only if their route is removed from the FIB. New sessions do a normal route lookup and use the preferred route through port1.
Community Discussion